Your datacenter is an application.
Scan it like one.
Keep the trusted base.Carry the evidence.
Security without another infrastructure operating system.
Run STRATUM on the Linux or Kubernetes foundation you already secure and operate.
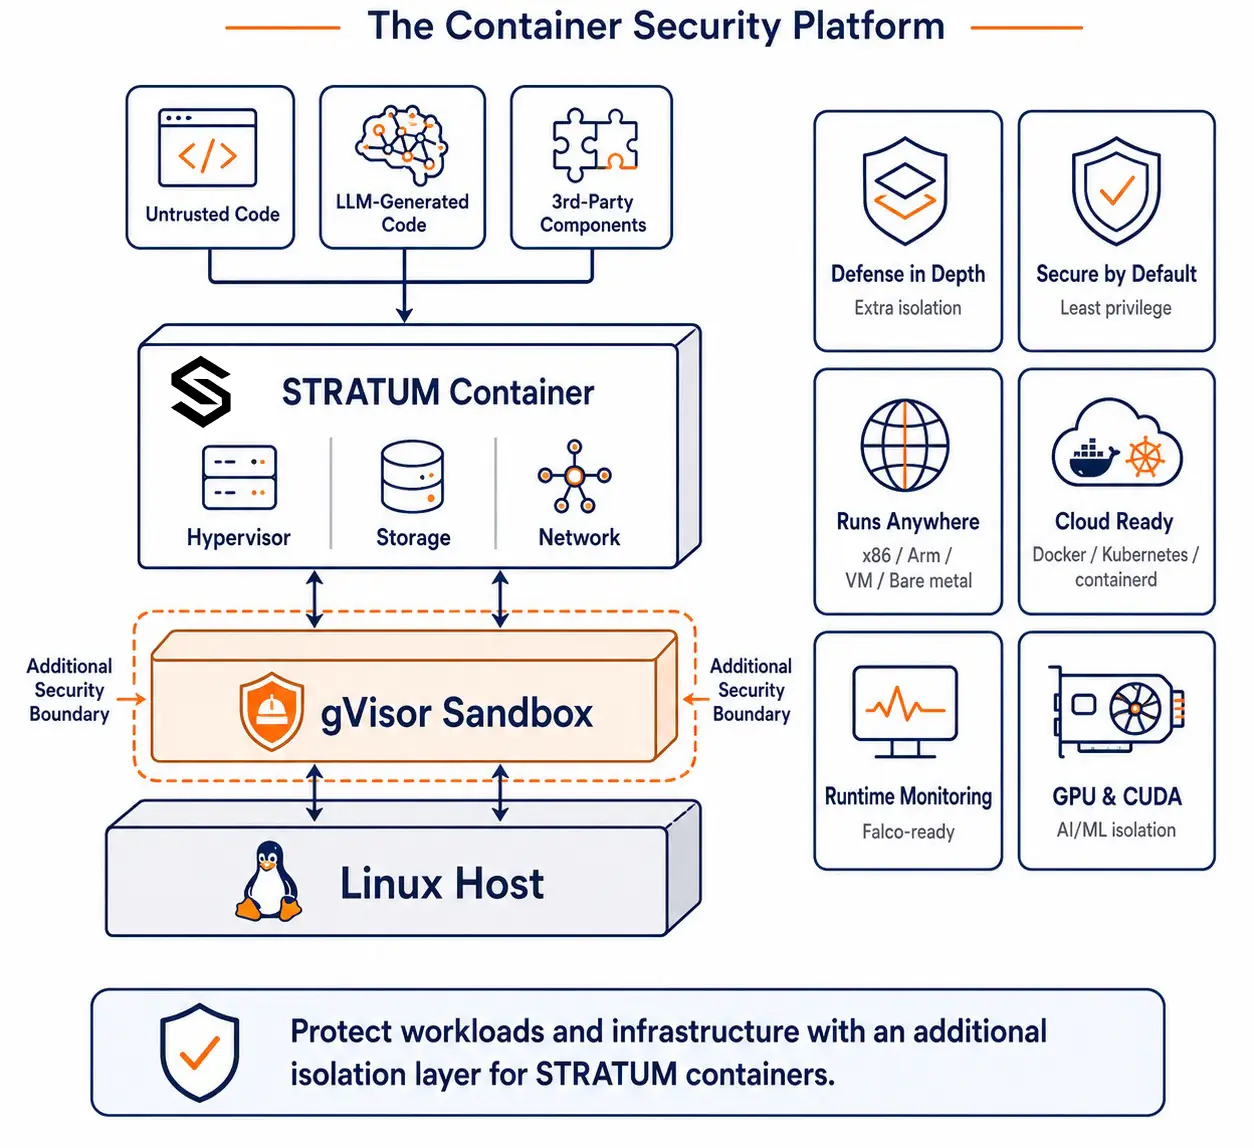
Keep what is already trusted.
STRATUM does not require a customer to replace an approved Linux foundation with another host operating system merely to get virtualization.
That keeps the adoption problem smaller and lets existing patching, scanning, hardening, backup, and observability practices remain relevant.
Security travels with the platform.
Security is part of how the artifact is built, scanned, promoted, and operated.
Trusted Base
Build on the Linux foundation already approved for the environment.
STRATUM uses a security-oriented container base and can be integrated into established Linux and Kubernetes operating models rather than creating another platform island.
IRON BANK BASEBody of Evidence
SBOMs, vulnerability evidence, and release identity belong with the artifact.
Use the exact image digest and software supply-chain evidence around the same infrastructure payload that will be promoted and deployed.
DOWNLOAD BASE REPORTSSPDXCYCLONEDXContinuum Cryptography
Security applies to the distributed fabric too.
Continuum Mesh is designed to use FIPS-approved cryptographic implementations for secure distributed connectivity. Enterprise deployment details and compliance evidence can be reviewed with the customer security team.
REQUEST SECURITY REVIEW